
Joe LoBianco has a fairly expansive definition of what it means to protect a bank.
As Executive Vice-President and Chief Information Security Officer at CIBC, LoBianco’s mandate stretches from the bank’s mission-critical systems and client data to third-party providers plugged into its infrastructure.
It is a significant scope, considering that CIBC serves more than 15 million clients in Canada and around the world. How it manages that already-wide remit continues to evolve as cyber threats become faster-moving and more sophisticated across the industry. Over the past year, AI has accelerated trends that cybersecurity teams were already watching, according to LoBianco.
“We’ve seen an increasing pace and sophistication of threats over time,” LoBianco said. “I would say AI is supercharging those.”
AI is changing the threat landscape
The threat landscape has changed, and so have the weak points that large enterprises need to watch. Historically, security teams could concentrate resources on the weaknesses judged to pose the greatest immediate risk, leaving lower-severity problems further down the remediation queue. LoBianco said AI is making that approach no longer viable.
“AI is particularly adept at chaining these lower-severity issues together into a much more high-risk weakness,” he said.
LoBianco said the industry has so far done a reasonably good job of keeping the most advanced tools out of malicious hands. Still, companies are beginning to see more AI-enabled attacks, giving threat actors greater ability to operate at speed and scale.
How banks are shifting their defences
Like many institutions, CIBC is looking beyond the highest-risk vulnerabilities and addressing lower-severity issues more quickly. The bank is also adjusting where it directs its cybersecurity attention and investment.
“We’ve seen an increasing pace and sophistication of threats over time. I would say AI is supercharging those.”
Joe LoBianco, CIBC
LoBianco pointed to several priorities, including embedding security earlier in the design of new products, increasing automated testing throughout the software development lifecycle, and strengthening how the bank manages risk across third-party providers. CIBC is also using AI to improve its security testing and defences, alongside core security practices such as patching, identity management, and data protection.
The pressure to respond to threats faster is also impacting the role security teams play inside large organizations. “We have to be building our defences to deal with this year’s and next year’s threats,” LoBianco added.
In addition to proactive threat monitoring, LoBianco said CIBC watches attacks and breaches affecting other organizations, examines which controls failed, and then asks how its systems would fare under similar circumstances.
These learnings also get applied to technology solutions that are built in-house.
“Within my team, our job is to figure out how we can help the business manage its risk, so what that means in practice is finding alternatives,” he said.
The bar for vendors is rising
No bank can solve every security problem in-house. Technology vendors enter the picture when banks can benefit from outside expertise, or when building a bespoke solution would make little sense. For high-growth companies hoping to fill those gaps, strong tech alone will not close the deal, according to LoBianco.
A security product might generate useful alerts, for example, but those alerts still have to feed into the systems and workflows a bank already uses to investigate and remediate issues. High-growth companies that understand those integration requirements early, LoBianco said, make adoption much easier for large enterprise customers.
“Do your homework,” LoBianco said. “Understand your customer and how they work.”
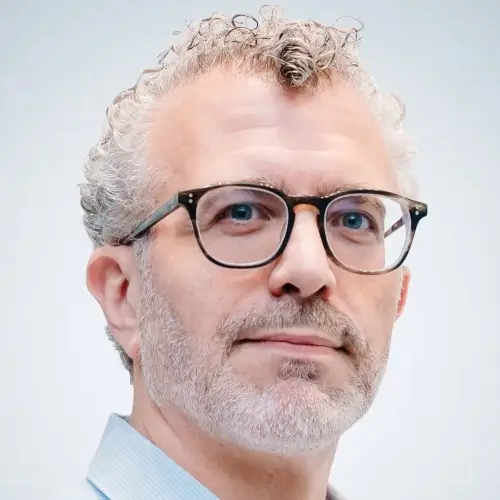
courtesy CIBC
In fact, seamless integration often outweighs marginal gains in product performance. “If it’s hard for us to integrate into our security practices, then it doesn’t matter if it’s two percent better than the other solution,” LoBianco added. “Our time to market is going to be impacted.”
Sean Duffy, Managing Director at CIBC Innovation Banking in the UK and Europe, sees the same challenge from the market side. Selling technology into a major financial institution can be a long process, Duffy said, because purchasing decisions involve more stakeholders and considerably more complexity than they might at a smaller organization.
“It can take years to sell some of these solutions,” Duffy said, adding that technology founders need to account for those timelines when thinking about funding and go-to-market strategy.
Duffy said buyers also want to know how a product will evolve with AI, who else is already using it, and—echoing LoBianco—how difficult it will be to integrate. LoBianco said the bar rises considerably when a bank’s data moves to a vendor’s systems. Companies need to prove they can maintain the required level of protection throughout the relationship.
Expectations around vulnerability remediation are accelerating, too. LoBianco feels that the new expectation is for “near real-time turnaround” when weaknesses are discovered in technology running in sensitive environments.
“That’s a very different bar than I think we had in the past, where we could wait days, if not weeks, for fixes from technology founders,” LoBianco said. “Now, it’s going to be a 24-hour-or-less turnaround. We need to have confidence that a provider is going to be able to do that for us today, during the sales cycle, but a few years down the road as well.”
Still, higher expectations have not diminished the role of outside technology founders. For many large enterprises, Duffy said, building software is simply not their core business.
“Companies are born to fill customer needs. And the vast majority focus on needs that are completely unrelated to software development. They have their hands full managing their own mandates; becoming a software development shop on top of that is not realistic and represents a diversion from core business focus.” Duffy added.
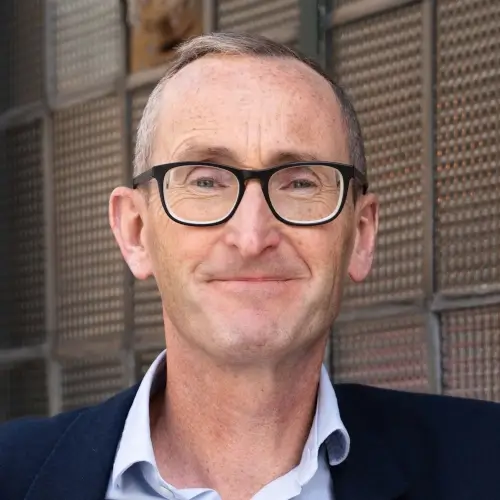
courtesy CIBC.
LoBianco said trying to develop every product internally at CIBC would not be practical from either a time or cost perspective. Outside technology founders remain an important part of CIBC’s ecosystem, and the bank is looking for a collaborative relationship with them.
“What’s changing is that I’m looking for more co-development, probably, than we used to,” LoBianco said. “We’re looking for design and development partners, as opposed to a series of vendors that I’m just buying shrink-wrapped, off-the-shelf software from.”
LoBianco and Duffy landed on much the same advice for founders: understand your customer, solve a real problem, adapt as the needs of your customers change, and be prepared for multiple go-to-market motions.
“If you have use cases for your product set that can suit other industries or other areas of [financial services], don’t neglect that,” Duffy said. “Don’t disregard that, because if you win a contract with a large bank like CIBC, that’s great, but it can take two, three years to get that.”
The broader point, Duffy said, is that patience should be part of the strategy, rather than a reason to narrow the opportunity.
“Selling into financial institutions and large banks can be challenging,” he added. “So be ready for the journey.”
But the journey is often well worth it. Winning the trust of a financial institution gives a young technology company credibility that carries well beyond a single contract. Banks also invest considerable time and resources into evaluating and integrating new technology, and those relationships tend to last.
CIBC sees its technology providers as long-term partners, rather than vendors it can easily swap out. For those willing to play the long game, the payoff can be years of reliable business. Few sectors offer companies the same combination of customer scale, spending power, and long-term demand.
PRESENTED BY
CIBC Innovation Banking combines specialized financing with sector expertise to help ambitious technology companies scale into larger markets. Learn more.
Feature image courtesy CIBC.